
How to Switch Password Managers on Android Without Exporting Your Passwords
Use the steps below as a working procedure and verify the feature availability on your device or account before changing security or account settings.
Quick steps
- Update Android and both password manager apps before starting the transfer.
- Install or open the password manager you want to use as the destination.
- Choose Import or Copy from another provider and let Android detect compatible managers.
- Review the source manager and explicitly authorize the transfer when Android sends you back to it.
- Confirm passwords and passkeys are present in the new manager before removing the old one.
- Keep the old manager installed until you have tested important accounts and recovery methods.
Before you move the vault
- Check that the old manager still opens and that you can authenticate without relying on autofill.
- Update Android and the destination manager before starting the transfer.
- Keep recovery information available before removing anything from the old vault.
- Test important accounts after migration rather than assuming that a successful import means every credential works.
My practical check
I would not delete the old vault immediately. I would first sign in to the destination on the phone and on one other device, then test the accounts I use most often. That pause makes recovery much easier if one credential or passkey did not transfer as expected.
A migration is not finished when the import button says it is finished. It is finished when the important accounts have been tested and the recovery path still works.
Best fit
Use the direct Android transfer flow when your old and new managers support it. Google says the newer experience moves passwords and passkeys without requiring an unencrypted export file.Compatibility
The published Android flow supports Android 8 and later. Availability still depends on the managers installed on the device and the rollout of their integration.Safety rule
Do not delete the old manager immediately. Verify high-value accounts, passkeys, autofill and recovery access first.Changing a password manager used to mean choosing between a clumsy migration and a risky export file. A common workflow was to export credentials into a file and then import that file into the replacement service. The problem was not only inconvenience. A password export can contain a large portion of a person’s digital identity in a format that is easy to copy and difficult to protect once it leaves the password manager. Google’s September 2026 Android update changes that workflow by allowing compatible password managers to hand the migration to Android itself.
The practical difference is important. You still decide which provider becomes the destination and you still authorize access in the existing manager, but the operating system coordinates the transfer instead of forcing you to move a credential file through storage. Google says the new experience can move both passwords and passkeys and is already available with Google Password Manager, 1Password, Bitwarden Password Manager and Dashlane, with additional partners expected to follow.
This guide explains the direct method first, then covers two fallback approaches for situations where the direct Android flow is not offered. The goal is not to make the migration sound more automatic than it is. A password manager change is a security operation. You should treat the old manager as the source of truth until the replacement has been checked account by account.
Before you start
Make a short inventory before touching your credentials. You do not need a spreadsheet for every login, but identify the accounts that would cause the most damage if you lost access: your primary email, banking and payment services, cloud storage, domain registrar, work systems, password manager account itself and any developer services that use passkeys or security keys. These are the accounts you should test first after migration.
Android
Install pending system updates and make sure the phone can unlock normally. The new transfer experience is designed for Android 8 and later.Destination app
Install the password manager you want to move to and sign in to the correct account before starting the import.Source app
Keep the old manager installed and signed in. You will normally be returned to it to review and authorize the transfer.It is also worth checking whether your destination manager has an account recovery method that you understand. A migration does not fix a weak recovery plan. If the destination account is protected by a master password plus a second factor or passkey, make sure those controls are available before you remove the old manager.
Method 1: Use Android’s direct password and passkey transfer
This is the preferred route when both managers support the new Android integration. Google describes a three-stage process: start the move in the new manager, let Android identify compatible managers, then return to the old manager to review and authorize the transfer.
Step 1: Open the new password manager
Install the destination password manager from the official app store and sign in. Look for an option labelled Import, Move, Transfer, Copy from another provider or similar wording. The exact label belongs to the individual password manager, so do not assume every application will use the same menu name. The important signal is that the app offers an Android-managed transfer rather than asking you to create a plain text export first.
Step 2: Let Android find the source manager
When the destination manager hands the task to Android, the operating system can detect compatible password managers already installed on the phone. This is the point where the migration stops being a simple app-to-app import and becomes an operating-system-coordinated transfer. If the old manager appears, select it. If it does not appear, do not start creating export files immediately. First confirm that the old manager is installed, signed in and supported by the current integration.
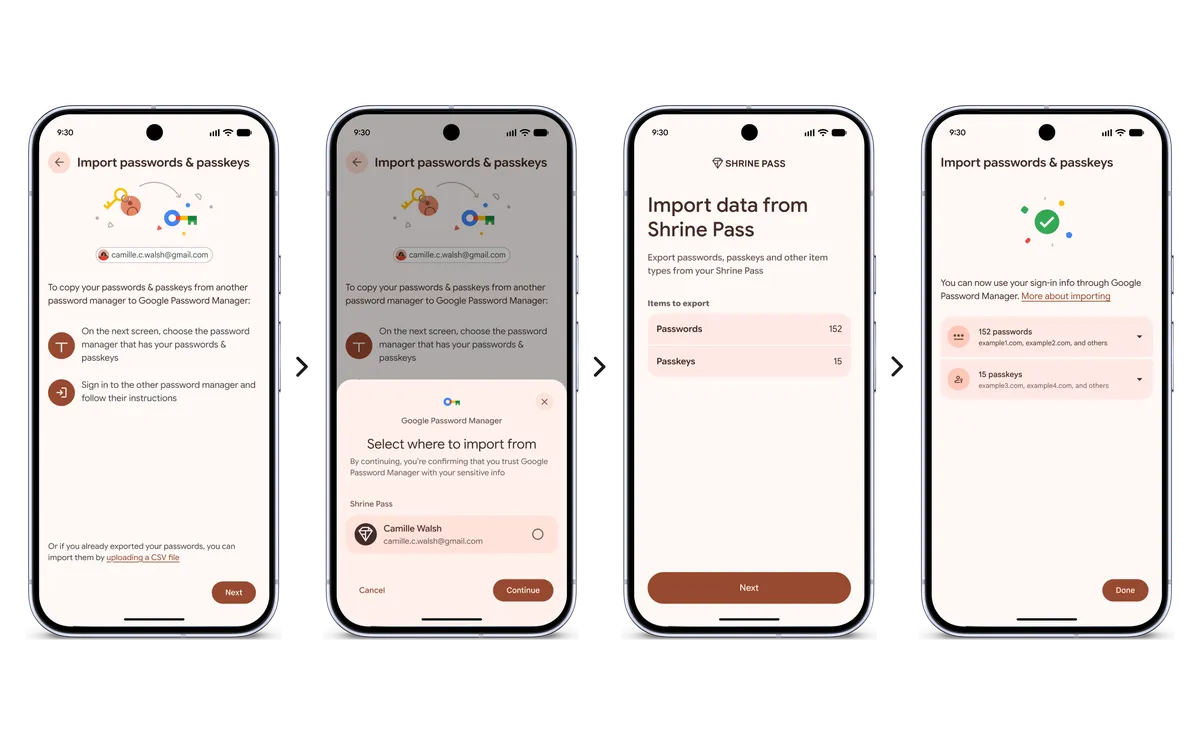
Step 3: Review and authorize
Android sends you back to the existing password manager so you can select, review and authorize the transfer. Read the confirmation screen rather than treating it as a formality. You are approving movement of sensitive credentials, and this is the last useful point at which you can stop if the source or destination looks wrong.
Step 4: Verify the destination
After the transfer finishes, open the destination manager and search for a small sample of credentials from different categories. Check a normal website login, a high-value account, an entry with a saved username and an account that uses a passkey if you have one. Do not rely on the item count alone. A successful count does not prove that every passkey, URI, username or autofill field is usable.
A migration is complete when the new manager can actually authenticate you, not when the import screen says it has finished.
Method 2: Use the destination manager’s supported import tool
If Android does not show the source manager, check the destination manager’s own import options. Some providers support direct imports from another password manager or provide a controlled migration path through their account settings. The key difference is that you should use the provider’s current documented workflow rather than downloading a generic CSV or text file from an unknown page.
This method is especially useful when the two providers have not yet completed their Android integration. It can also be useful on a secondary device where the new transfer interface has not reached the same release channel. The exact menu names and supported source managers change over time, so use the destination provider’s current help documentation before beginning.
Method 3: Use an export file only as a fallback
A file-based migration remains a practical fallback when a direct transfer is unavailable, but it should be treated as a controlled security procedure. Exporting passwords can create a highly sensitive file. Keep it off shared folders, do not upload it to cloud storage for convenience and do not leave it in Downloads after the import. If the provider supports an encrypted export format, use that rather than a plain text format.
Once the destination manager confirms the import, delete the temporary export securely and check the recycle bin or trash as appropriate. If the file was ever copied to another device or backup service, account for those copies too. The objective is to reduce the number of places where the credential dataset exists.
How to verify passkeys after migration
Passkeys need a different verification mindset because there may be no visible password to compare. Open several accounts that you know use passkeys and test sign-in from a fresh session. If the browser offers the new manager as a credential provider and the passkey authenticates without falling back to the old manager, the migration is behaving as intended. Do not delete the old manager until the accounts that matter most have passed this test.
Also check the account security page itself. Many services show a list of registered passkeys or security credentials. Use that page to confirm that the credential you expect to use still exists. If the service shows multiple old and new passkeys, do not remove an older credential until you know the new one works on another device or through the service’s recovery process.
Windows, macOS and iPhone considerations
The new Android experience is specifically an Android operating-system feature. If you are moving between devices, treat the phone transfer and the broader account migration as separate tasks. On Windows and macOS, the password manager’s desktop application or browser extension may have its own import and sync behaviour. On iPhone and iPad, the available migration path depends on iOS support from the password manager and the provider’s current import capabilities.
Windows
Install the destination manager and browser extension only after you know the correct account. Verify autofill in a test login before removing the previous extension.macOS
Check the destination app and browser extension separately. A credential may be present in the vault while the browser has not yet been granted autofill permission.iPhone and iPad
Use the destination manager’s iOS instructions and confirm the system password provider setting if the app needs to become the default credential provider.If you use the same password manager across platforms, complete the migration on one device first and allow synchronization to settle before changing every device. A staged migration is easier to troubleshoot than changing the source and destination simultaneously across a phone, laptop and tablet.
Common problems and fixes
The old manager is not listed
Update both apps, reopen them and confirm the old manager is installed and unlocked. If the integration still does not appear, use the destination provider’s supported import path.Some passkeys are missing
Check whether the affected accounts use a passkey type supported by both providers. Test the account directly before deleting the source credential.Autofill works in one browser only
Check the operating system password provider setting and the browser’s autofill permissions. Vault data and browser permissions are separate layers.If you are already troubleshooting browser autofill or sync, COMPSMAG’s guide to Chrome sync issues covers a different but related Chrome problem and can help you separate browser state from account state.
A safer migration checklist
- Keep both password managers available during verification.
- Test your primary email before anything else.
- Test at least two passkey accounts if you use passkeys regularly.
- Confirm browser autofill on the devices you actually use.
- Check account recovery methods before removing the old manager.
- Delete any temporary export file if you used the fallback method.
- Only remove the old manager after the destination has proved reliable.
The new Android transfer system removes one of the worst parts of a password manager migration: the need to create a large unencrypted credential file just to move providers. It does not remove the need for verification. Your job is still to confirm that the new vault contains the credentials you depend on and that the operating system, browser and apps can actually use them.
My practical way to handle the migration
I am deliberately treating a password manager change as a security migration rather than a normal app switch. That distinction matters because the vault can contain years of logins and because passkeys do not behave like ordinary password fields. I was initially tempted to think the job was finished once the new manager showed the expected number of entries, but that is too shallow a check. The useful question is whether the accounts still work, whether the new provider is handling autofill correctly and whether I can recover access if the new device or account fails.
My first rule is simple. I keep the old manager available until the new one has survived a real test. I do not make the old vault disappear just because the import screen says it completed. I choose a few accounts that represent different situations, such as a normal password login, an account protected by a passkey and a service where recovery codes or another second factor are important. That small sample catches problems that a raw item count can miss.
Before moving anything
Update both managers, confirm you know the destination account credentials and make sure your recovery method works before starting.
After the transfer
Test autofill, a high-value login, a passkey and synchronization on another trusted device before removing the old vault.
There is also a useful distinction between moving credentials and changing the password itself. The Android transfer experience is about moving stored credentials between compatible providers. It is not a reason to rotate every password at the same time. If an account is already secure, changing it during migration can add unnecessary work and make troubleshooting harder. I prefer to separate those jobs. First establish that the new vault is complete and usable. Then rotate individual credentials only when there is a separate security reason to do so.
If a passkey behaves differently after migration, I would not immediately assume the transfer failed. Passkeys involve the credential provider, the operating system and the website or app. Check the destination manager, confirm that the account recognises the credential and perform a fresh sign-in. If the service offers a security page showing registered passkeys, that page is a useful second source of truth. A visible entry in the vault alone does not prove that the website can authenticate with it.
A successful migration is not the moment the import finishes. It is the point at which the new manager becomes the trusted source and the important accounts have been verified.
For people using Android alongside Windows or macOS, I would also check the desktop layer separately. The mobile manager can be perfectly healthy while a browser extension is signed out, disabled or still configured to use another password provider. Check the browser extension, system autofill setting and desktop application independently. If one device behaves differently, change one setting at a time instead of reinstalling everything.
Verification after the transfer
Do not judge a password migration by the number shown on the import screen. A vault can contain the expected number of entries while an important field or passkey still needs attention. Start with the account that protects your other accounts, then test a second high-value service and one ordinary login. This gives you a practical sample across different credential types.
Browser autofill is a separate layer from the vault. On Android check the system password provider and then check the browser. On Windows and macOS check the extension permissions as well. If the new manager contains the credential but the browser never offers it, the problem is usually integration or permission rather than missing data.
Passkeys deserve a fresh sign-in test because there is no password string to compare. Open the account security page where possible and confirm that the new credential is present. Then sign out and authenticate again. A successful fresh sign-in is stronger evidence than simply seeing a passkey entry in the vault.
When the direct transfer is unavailable
If Android does not list the old manager, update both applications and confirm that both accounts are signed in. If the source still does not appear, check the destination provider documentation for a supported direct import. Do not immediately create several export files because each file is another copy of your credential dataset.
If an export is unavoidable, use the most protected export format offered by the provider. Treat the resulting file as sensitive data. Do not email it to yourself, upload it to a public folder or leave it in a shared Downloads directory. Import it promptly and remove the temporary file after verifying the destination.
A staged migration is safer than changing every device at once. Move the vault on one phone, test it, then let synchronization reach your other devices. After that, replace browser extensions and desktop applications one at a time. This makes it much easier to identify which layer is responsible if autofill or passkeys behave differently.
Finally, keep the old manager until you can recover the new manager account independently. If the destination account becomes inaccessible and the old manager has already been removed, a successful import can still leave you locked out. Recovery planning is part of the migration rather than a task to do after it.
The September Android transfer feature removes much of the unsafe file handling that used to accompany password manager changes. It does not remove the need for verification, staged rollout and recovery planning. Those controls remain the user’s responsibility.
Frequently Asked Questions
Can I switch password managers without exporting a CSV file?
Yes when the Android transfer path is available for the managers involved. The direct route avoids creating an extra credential file.
Should I delete the old password manager immediately?
No. Keep it until the destination has been tested on the devices and accounts that matter most to you.
What should I test after moving passwords?
Test several passwords, autofill forms and important passkeys or recovery methods. The exact checks depend on what the source manager stored.
What if the destination manager does not appear in Android?
Update both applications, confirm the correct accounts are signed in and check the destination provider documentation for supported migration options.
Is a password export safe to keep in Downloads?
Treat it as sensitive data. Protect the export, import it promptly and remove the temporary copy after verifying the destination.
Can I migrate one device first?
Yes. A staged migration is easier to troubleshoot because you can confirm the destination before changing every device.